GDPR

BrandPost: Using RPA to Efficiently and Effectively Meet Compliance Demands

Meeting regulatory compliance requirements has become labor-intensive and a costly aspect of doing business within almost every industry sector. Organizations must navigate a complex matrix of local, state, national, and international regulations, with some applied universally, others on an  industry-specific basis.Whether it’s the European Union’s General Data Protection Regulation (GDPR), the United States’ Health Insurance…

Meeting regulatory compliance requirements has become labor-intensive and a costly aspect of doing business within almost every industry sector. Organizations must navigate a complex matrix of local, state, national, and international regulations, with some applied universally, others on an  industry-specific basis.Whether it’s the European Union’s General Data Protection Regulation (GDPR), the United States’ Health Insurance Portability and Accountability Act (HIIPA), or California’s air quality standard laws, failure to comply with these and of hundreds of other regulatory demands can result in significant fines, reputational damage, and lost revenue. In short, the costs of non-compliance can rapidly outpace the expense of adhering to all relevant regulatory mandates.To read this article in full, please click here
Read More

Be the first to write a comment.

Leave a Reply

Your email address will not be published. Required fields are marked *

GDPR

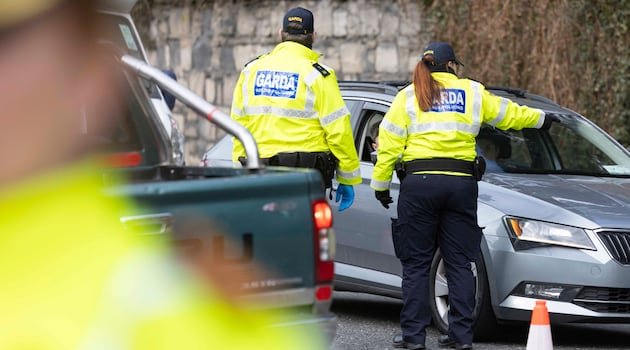
Seven years after asking, gardaí cannot access driving licence photos

Ability to confirm drivers’ identity with photographs omitted from legislation due to ‘complex’ GDPR rules…

Ability to confirm drivers’ identity with photographs omitted from legislation due to ‘complex’ GDPR rules…
Read More

Continue Reading
GDPR

Google fined €403 million over location data privacy violations

Ireland’s Data Protection Commission (DPC) has fined Google €403 million ($463M) for multiple GDPR violations related to processing users’ location data. …

Ireland’s Data Protection Commission (DPC) has fined Google €403 million ($463M) for multiple GDPR violations related to processing users’ location data. …
Read More

Continue Reading
GDPR

Google fined €403m by Ireland’s Data Protection Commission for GDPR breaches

Follows investigation into how the company processed location data…

Follows investigation into how the company processed location data…
Read More

Continue Reading
GDPR

GDPR wasn’t designed for AI and that’s a security problem

The Security Think Tank explores the intersection of GDPR and artificial intelligence, considering how data protection standards in the UK and Europe are changing in this new paradigm…

The Security Think Tank explores the intersection of GDPR and artificial intelligence, considering how data protection standards in the UK and Europe are changing in this new paradigm…
Read More

Continue Reading