New DIFC Law expected to bring enhanced governance and transparency obligations

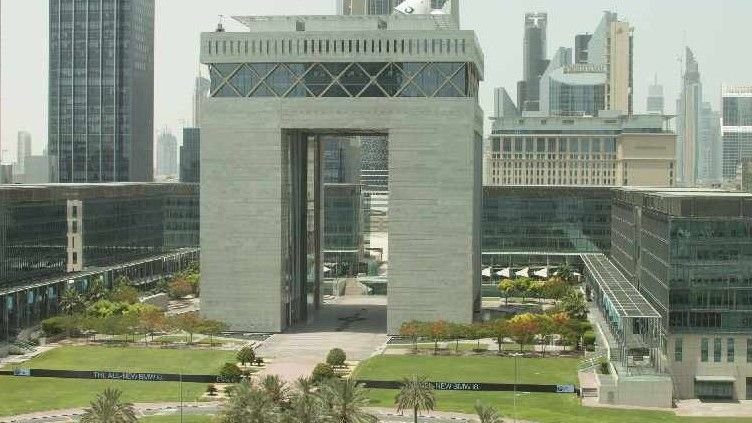
The new Dubai International Financial Centre (DIFC) Data Protection Law (DPL) 2020 law, coming into effect from July 1, is expected to bring enhanced governance and transparency obligations.
Even though the law comes into force from July, businesses to which the law applies will have a grace period of three months, until October 1, 2020, giving organisations just a few months to make necessary changes required to bring compliance frameworks into line with the new law.
The new Data Protection Law replaces Data Protection Law DIFC Law No 1 of 2007, which was already one of the most advanced in the region, places Dubai and DIFC at the forefront of data protection in the region and enabling the financial hub to enhance the Centre’s data protection practices related to global data, security and privacy best practice.
It is now more important than ever for companies to have a data management strategy to ensure data compliance is taking place within an organisation – both from an operational and cultural perspective.
By encouraging data responsibility and implementing the latest data management tools, businesses can do their bit in preparing themselves for DPL 2020.
The new DPL 2020 law will actively benefit companies in a range of ways. Not only will it manage data effectively and ensure data compliance, but it will also increase companywide efficiency; provide a competitive advantage and protection against malware attacks.
The new DIFC Law reflects many of the requirements of the EU’s General Data Protection Regulation (GDPR) seen by many as the ‘gold standard’ for data protection compliance.
“From our previous experience in preparing for the GDPR coming into force, we recommend that organisations should start planning now. In particular, organisations should prioritise fact gathering and other time-intensive tasks such as contract remediation,” Kellie Blyth, head of Data and Technology at Baker McKenzie, said.
However, she said that there are some key differences between the GDPR and new DIFC Law, which organisations should be aware of.
“The new DIFC Law requires Controllers and Processors to appoint a DPO [data protection officer] if they carry out high-risk processing activities on a systematic or regular basis or if required to do so by the Commissioner.
“If a Controller or Processor is not required to appoint a DPO, the organisation must allocate responsibility within its organisation for oversight and compliance with its data protection obligations under the new DIFC Law (or any other applicable data protection law),” she said.
Time to act
The DPO must reside in the UAE, Blyth said unless the DPO is employed within the organisation’s group and performs a similar function for the group on an international basis.
Blyth urged organisations in the DIFC to move swiftly to review their current data processing practices and to identify where their existing data protection policies and procedures will need to be updated to reflect the requirements of the new law.
“An important difference between the new DIFC Law and the GDPR is that DPOs are required to conduct an annual assessme
Be the first to write a comment.


