Internet Security

Privacy complaints received by tech giants’ favorite EU watchdog up more than 2x since GDPR

A report by the lead data watchdog for a large number of tech giants operating in Europe shows a significant increase in privacy complaints and data breach notifications since the region’s updated privacy framework came into force last May. The Irish Data Protection Commission (DPC)’s annual report, published today, covers the period May 25, aka…


A report by the lead data watchdog for a large number of tech giants operating in Europe shows a significant increase in privacy complaints and data breach notifications since the region’s updated privacy framework came into force last May.

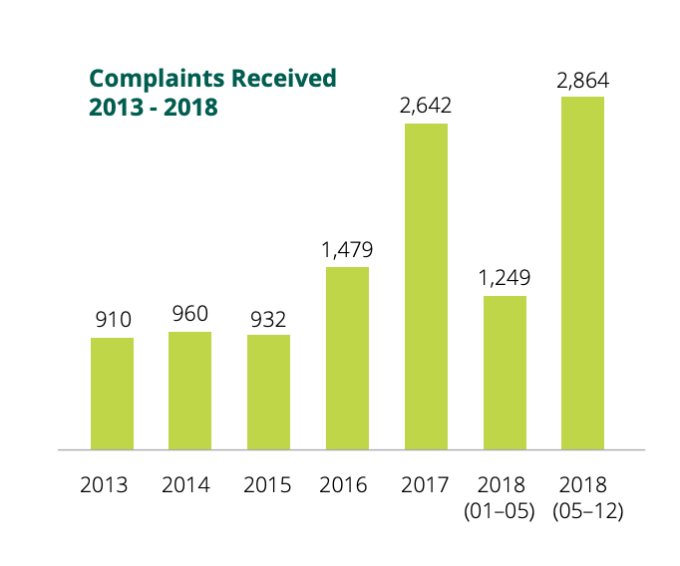
The Irish Data Protection Commission (DPC)’s annual report, published today, covers the period May 25, aka the day the EU’s General Data Protection Regulation (GDPR) came into force, to December 31 2018 and shows the DPC received more than double the amount of complaints post-GDPR vs the first portion of 2018 prior to the new regime coming in: With 2,864 and 1,249 complaints received respectively.

That makes a total of 4,113 complaints for full year 2018 (vs just 2,642 for 2017). Which is a year on year increase of 36 per cent.

But the increase pre- and post-GDPR is even greater — 56 per cent — suggesting the regulation is working as intended by building momentum and support for individuals to exercise their fundamental rights.
“The phenomenon that is the [GDPR] has demonstrated one thing above all else: people’s interest in and appetite for understanding and controlling use of their personal data is anything but a reflection of apathy and fatalism,” writes Helen Dixon,Ireland’s commissioner for data protection.

She adds that the rise in the number of complaints and queries to DPAs across the EU since May 25 demonstrates “a new level of mobilisation to action on the part of individuals to tackle what they see as misuse or failure to adequately explain what is being done with their data”.

While Europe has had online privacy rules since 1995 a weak regime of enforcement essentially allowed them to be ignored for decades — and Internet companies to grab and exploit web users’ data without full regard and respect for European’s privacy rights.

But regulators hit the reset button last year. And Ireland’s data watchdog is an especially interesting agency to watch if you’re interested in assessing how GDPR is working, given how many tech giants have chosen to place their international data flows under the Irish DPC’s supervision.

More cross-border complaints

“The role places an important duty on the DPC to safeguard the data protection rights of hundreds of millions of individuals across the EU, a duty that the GDPR requires the DPC to fulfil in cooperation with other supervisory authorities,” the DPC writes in the report, discussing its role of supervisory authority for multiple tech multinationals and acknowledging both a “greatly expanded role under the GDPR” and a “significantly increased workload”.

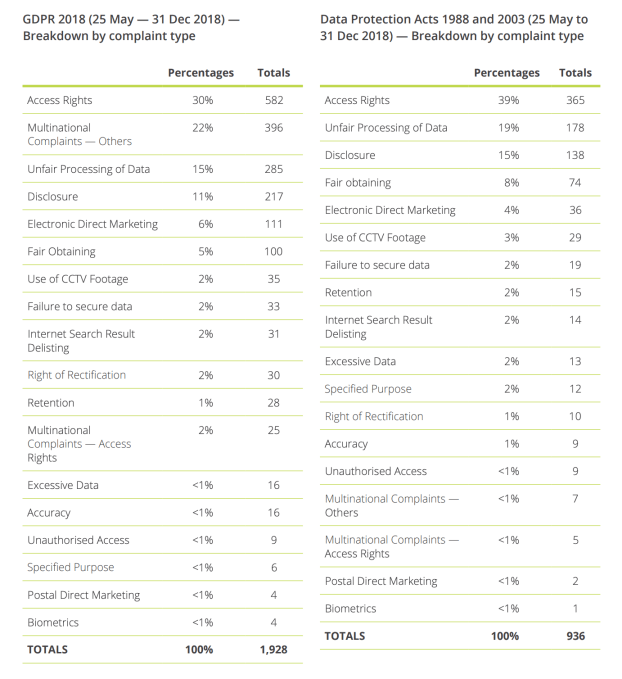
A breakdown of GDPR vs Data Protection Act 1998 complaint types over the report period suggests complaints targeted at multinational entities have leapt up under the new DP regime.

For some complaint types the old rules resulted in just 2 per cent of complaints being targeted at multinationals vs close to a quarter (22 per cent) in the same categories under GDPR.

It’s the most marked difference between the old rules and the new — underlining the DPC’s expanded workload in acting as a hub (and often lead supervisory agency) for cross-border complaints under GDPR’s one-stop shop mechanism.

The category with the largest proportions of complaints under GDPR over the report period was access rights (30%) — with the DPC receiving a full 582 complaints related to people feeling they’re not getting their due data. Access rights was also most complained about under the prior data rules over this period.

Other prominent complaint types continue to be unfair processing of data (285 GDPR complaints vs 178 under the DPA); disclosure (217 vs 138); and electronic direct marketing (111 vs 36).
EU policymakers’ intent with GDPR is to redress the imbalance of weakly enforced rights — including by creating new opportunities for enforcement via a regime of supersized fines. (GDPR allows for penalties as high as up to 4 per cent of annual turnover, and in January the French data watchdog slapped Google with a $57M GDPR penalty related to transparency and consent — albeit still far off that theoretical maximum.)

Importantly, the regulation also introduced a collective redress option which has been adopted by some EU Member States.

This allows for third party organizations such as consumer rights groups to lodge data protection complaints on individuals’ behalf. The provision has led to a number of strategic complaints being filed by organized experts since last May (including in the case of the aforementioned Google fine) — spinning up momentum for collective consumer action to counter rights erosion. Again that’s important in a complex area that remains difficult for consumers to navigate without expert help.

For upheld complaints the GDPR ‘nuclear option’ is not fines though; it’s the ability for data protection agencies to order data controllers to stop processing data.

That remains the most significant tool in the regulatory toolbox. And depending on the outcome of various ongoing strategic GDPR complaints it could prove hugely significant in reshaping what data experts believe are systematic privacy incursions by adtech platform giants.

And while well-resourced tech giants may be able to factor in even very meaty financial penalties, as just a cost of doing a very lucrative business, data-focused business models could be far more precarious if processors can suddenly be slapped with an order to limit or even cease processing data. (As indeed Facebook’s business just has in German

Read More

Be the first to write a comment.

Leave a Reply

Your email address will not be published. Required fields are marked *

Internet Security

Artists can express humanitarian concerns, but not undermine public order and security: Tan Kiat How

Advertisement Singapore Artistes can express humanitarian concerns, but not undermine public order and security: Tan Kiat How Senior Minister of State Tan Kiat How cited several performances dealing with social and humanitarian issues that had been allowed to proceed in Singapore. Robert Del Naja and Grant Marshall from Massive Attack stand with a Palestinian flag

Advertisement

Singapore

Artistes can express humanitarian concerns, but not undermine public order and security: Tan Kiat How

Senior Minister of State Tan Kiat How cited several performances dealing with social and humanitarian issues that had been allowed to proceed in Singapore.

Artistes can express humanitarian concerns, but not undermine public order and security: Tan Kiat How

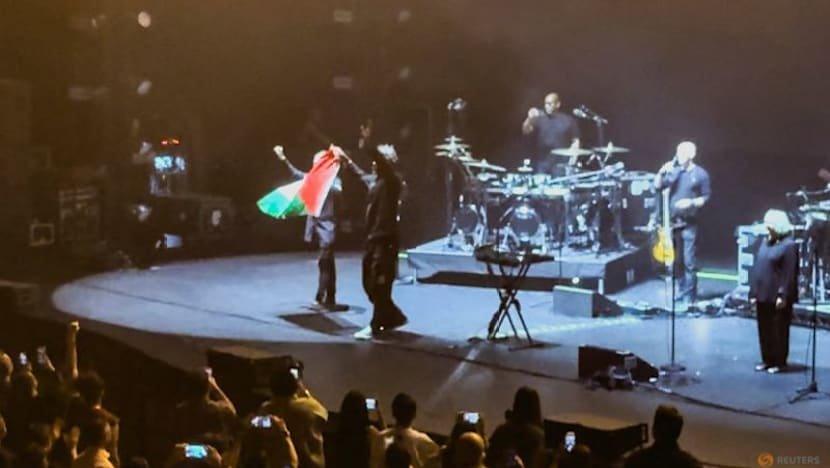
Robert Del Naja and Grant Marshall from Massive Attack stand with a Palestinian flag onstage at the end of their performance in Singapore, July 29, 2026, in this screengrab from video obtained from social media. Simran Panaech/via REUTERS


New: You can now listen to articles.


This audio is generated by an AI tool.

Justin Ong Guang-Xi

Justin Ong Guang-Xi

Justin Ong Guang-Xi

10 Sep 2026 01:42PM
(Updated: 10 Sep 2026 02:06PM)


Bookmark


Bookmark


Share

SINGAPORE: Artistes can express humanitarian concerns about international conflicts, but such expression should not undermine public order, security or stability in Singapore, Senior Minister of State for Digital Development and Information Tan Kiat How said on Thursday (Sep 10).

“Singapore should not be used by foreigners as a platform to further political causes, including those relating to conflicts or political issues overseas,” he said.

Artistes, whether Singaporean or foreign, are expected to abide by Singapore’s laws and the conditions of the arts entertainment licence when performing here, he added.

Mr Tan was responding in parliament to MP Hazlina Abdul Halim (PAP-East Coast), who asked how authorities distinguish prohibited political advocacy from expressions of humanitarian concern.

CNA Games
Guess Word
Guess Word
Crack the word, one row at a time

Buzzword
Buzzword
Create words using the given letters

Mini Sudoku
Mini Sudoku
Tiny puzzle, mighty brain teaser

Mini Crossword
Mini Crossword
Small grid, big challenge

Word Search
Word Search
Spot as many words as you can

Show More

Show Less

She also asked how an artiste’s intent and the context of an expression are taken into account, and whether licensing conditions would be reviewed to exclude peaceful expressions of support for humanitarian causes.

Mr Tan said that besides an artiste’s intention, the Infocomm Media Development Authority (IMDA) considers the likely impact of a performance when assessing whether it meets licensing conditions.

Under IMDA’s Arts Entertainment Classification Code, content should not undermine public order, national security or stability.

The code, which sets out the framework for assessing and classifying live or public arts entertainment, also states that content should be “sensitive to the concerns of different racial or religious groups and the prevailing community expectations of what is necessary to safeguard racial harmony and religious harmony”.

In July, members of British band Massive Attack were issued stern warnings and barred from re-entering Singapore after flying a Palestinian flag during a concert, with one of the members shouting “Free Palestine”.


06:31 Min

The government recognises the humanitarian impact of international conflicts and that artistes may wish to express concern for those affected. Such expressions are not prohibited but should not undermine public order, national security or stability in Singapore. This condition is made clear in the Arts Entertainment Classification Code issued by the Infocomm Media Development Authority. Senior Minister of State for Digital Development and Information Tan Kiat How highlighted this approach in reply to an MP’s questions in parliament on Thursday (Sep 10). He stressed that Singapore should not be used by foreigners as a platform to further political causes, including those relating to conflicts or political issues overseas. 

Ms Hazlina asked Mr Tan for examples of performances involving social causes that had been allowed to take place.

He cited To The Unforgotten, an event held in May this year that featured a song, poem and multimedia artwork about the Israel-Gaza conflict. It was classified R18.

Another example was 6 Microlectures on Genocides. Also classified R18, the play comprised short works that explore themes of genocide, war crimes and contemporary conflicts, Mr Tan said.

He also pointed to the 2024 stand-up comedy show Namaste, which was classified Advisory 16 and included a segment in which comedians spoke about the Israel-Gaza conflict.

“So having material and content on causes itself is not prohibited, and the licensing framework is designed to, of course, protect young people from unwanted content, but also allow people to make decisions on what they can watch,” said Mr Tan.

“But at the same time, having some boundaries on the kind of content that may stir up public disorder or national security considerations.”

Mr Tan said assessments were “very contextual” and encouraged applicants for Arts Entertainment Licences to engage IMDA early.

“The earlier the applicants engage IMDA, the earlier conversations can start, and earlier we can give clarity and guidance on the kind of content that may be approved and

!–>!–>
Read More

Continue Reading
Internet Security

Trezor Email Provider Breached in Phishing Attack Targeting Crypto Users

Trezor warned users that attackers used a compromised third-party email provider to send a fake STM32 security alert, a phishing scam that also hit rival BitBox and other Bitcoin companies. The post Trezor Email Provider Breached in Phishing Attack Targeting Crypto Users appeared first on Crypto News Australia…

Trezor warned users that attackers used a compromised third-party email provider to send a fake STM32 security alert, a phishing scam that also hit rival BitBox and other Bitcoin companies.
The post Trezor Email Provider Breached in Phishing Attack Targeting Crypto Users appeared first on Crypto News Australia…
Read More

Continue Reading
Internet Security

Liquid ‘white hats’ return $270M in Bitcoin as network prepares restart

The actors returned 85% of the Bitcoin withdrawn from Liquid’s federation wallet following the security incident…

The actors returned 85% of the Bitcoin withdrawn from Liquid’s federation wallet following the security incident…
Read More

Continue Reading
Internet Security

Six Egyptian Men Arrested Following Abduction and Sexual Assault Video

Security authorities in Giza have arrested six individuals, including five students and a delivery worker, following the viral spread of a social media video depicting the violent abduction of a young woman in broad daylight. Investigators tracked down the victim, who lives in the Al-Ahram area…

Security authorities in Giza have arrested six individuals, including five students and a delivery worker, following the viral spread of a social media video depicting the violent abduction of a young woman in broad daylight. Investigators tracked down the victim, who lives in the Al-Ahram area…
Read More

Continue Reading