Processors (CPUs) provide the brainpower for all the computerized devices we use day to day, from PCs and smartphones down to mundane things such as ATMs. Therefore an exploit – or exploits – that affects virtually all of these devices at the same time is a shocking thing to hear about.
Unfortunately, early 2018 saw just such a thing happen with the news that a design flaw in nearly all modern processors had been found.
What are Meltdown and Spectre?
Meltdown and Spectre are the names given to the two newly discovered vulnerabilities that affect virtually every device with a processor in it.
They rely on retrieving small amounts of data that are made available outside of the processor temporarily. This happens due to a design in processors called “speculative execution”.
This is the process where a CPU essentially guesses what information it will need next to function quickly.
Spectre allows attackers to force the processor itself to start the speculative execution process. They then access the extra data to obtain sensitive information that should never be available.
Meltdown fundamentally breaks down the mechanism that stops applications from accessing system memory. By doing so it enables exploits to access arbitrary system memory to retrieve sensitive data.
Who discovered them?
Both exploits were independently discovered by multiple teams of researchers.
Meltdown
Jann Horn (Google Project Zero)
Werner Haas, Thomas Prescher (Cyberus Technology)
Daniel Gruss, Moritz Lipp, Stefan Mangard, Michael Schwarz(Graz University of Technology)
Spectre
Jann Horn (Google Project Zero)
Paul Kocher in collaboration with Daniel Genkin (University of Pennsylvania and University of Maryland), Mike Hamburg (Rambus), Moritz Lipp (Graz University of Technology), and Yuval Yarom (University of Adelaide and Data61)
What systems are affected?
On a technical level, every Intel processor that implements out-of-order execution (speculative execution) is potentially affected. This includes almost all Intel processors dating back all the way to 1995!
A portion of AMD processors and ARM processors are also affected.
All desktop, laptop and cloud computing services may be affected by Meltdown.
Am I affected by Meltdown and Spectre?
Yes!
This may seem like a very blunt answer but due to the wide-reaching nature of the design flaw, you almost certainly have a device that will have been affected.
Does my antivirus protect me?
Antivirus programs could theoretically detect the use of these exploits, however, in practice it is very unlikely. It is possible that your antivirus could detect malware designed to exploit these vulnerabilities but not the actual vulnerabilities themselves.
How do I protect myself?
The Meltdown exploit is able to be fixed with a software patch as it relies on breaking the isolation between user apps and the operating system.
Computers fitted with a vulnerable processor and running unpatched operating systems will be open to exploit.
Fortunately, Operating system vendors have released relevant patches to protect their users. As long as you regularly update your operating system using built-in update tools, you should be fully protected from the Meltdown vulnerability.
As usual, it is best to operate safe web browsing habits and not install any potential malware on to your device that may potentially make use of these vulnerabilities.
Spectre has proven to be much harder to protect from as it is executed at the hardware level.
Initial advice so far is to follow the basic steps (similar to meltdown):
Update your operating system frequently
Install updates from your hardware manufacturer (firmware updates)
Turn on isolation mode in your web browser ( Chrome and Firefox ) – This prevents exploits in javascript from utilizing Spectre vulnerability.
What next?
The main thing for most people to do is to not panic. If you have followed the basic security steps and best practices above then you will almost certainly be safe.
It is important to note that some of the security patches that have been released may deliver a performance hit to your device. This is a widespread complaint and many of the operating system vendors recognize this as an issue.
They have stated that the performance hit should not be noticeable to the average user, however, hits to performance are “highly variable and depend on a number of factors”.
If you feel like your device performance has been significantly affected, do some research on whichever update you just installed. Other people may have suggestions and/or the vendor themselves may recognize a compatibility issue with certain device setups.
Conclusion
The shock release of these two huge vulnerabilities should be a wakeup call to the entire world.
It is increasingly important in this day and age to be ever vigilant about what information you store on your devices.
More importantly, users and companies should focus on preventative practices, such as being aware of potential malware that could expose devices to cybercriminals.
For more advice on what users should look out for in 2018, check our article – Internet security threats to look out for in 2018.
close Video Google general counsel explains AI-powered phishing rise Halimah Delaine Prado, Google General Counsel, reveals the rise of AI-powered phishing scams originating from China’s ‘outsider enterprise.’ She explains how these criminals use artificial intelligence to create highly convincing fake websites, impersonating trusted brands like T-Mobile to defraud hundreds of thousands of Americans, causing millions
Published
15 hours ago
in
By
close
Video
Google general counsel explains AI-powered phishing rise
Halimah Delaine Prado, Google General Counsel, reveals the rise of AI-powered phishing scams originating from China’s ‘outsider enterprise.’ She explains how these criminals use artificial intelligence to create highly convincing fake websites, impersonating trusted brands like T-Mobile to defraud hundreds of thousands of Americans, causing millions in losses. Prado highlights Google’s strategy to combat these evolving threats.
Apple is putting one of its most serious security warnings somewhere you are far less likely to miss it: right on your iPhone Lock Screen. Apple confirmed directly to CyberGuy that it sent a new wave of threat notifications last week, saying, “We can confirm threat notifications were sent on August 13 to targeted users in 110 countries, and to date we have notified users in over 150 countries in total.”
If one of these alerts suddenly appears on your iPhone, do not swipe it away and assume it is another routine security notice. Apple considers these high-confidence alerts that someone has specifically targeted you with unusually sophisticated spyware. Here’s what the warning means, how to verify it’s real and what to do next if Apple says you were targeted.
APPLE PAY TEXT SCAM THREATENS $8,250 LOSS IN 35 MINUTES
Apple sent mercenary spyware threat notifications to targeted iPhone users in 110 countries, with warnings now appearing directly on Lock Screens.(Kurt “CyberGuy” Knutsson)
New! Free live CyberGuy class: Protect Your Money From Today’s Biggest Threats
Join us Saturday, August 29, at 10 AM ET for a free CyberGuy LIVE class covering five simple steps to help defend yourself against AI scams, fraud, identity theft and financial hacks. Kurt “CyberGuy” Knutsson will explain how to set up bank alerts, strengthen your account logins, protect your phone number, freeze your credit and help secure your retirement savings against unauthorized transfers. No technical experience is needed. You’ll also receive our financial protection checklist, and every registrant will get a link to the class recording afterward.
Reserve your free spot today at CyberGuyLive.com.
What Apple’s new spyware warning looks like
Apple says it updated its threat notifications with a new user experience designed to make important information and recommended security steps easier for recipients to access. A threat notification can now appear directly on the iPhone Lock Screen and in Settings. Apple also sends an email to addresses associated with your Apple Account. In addition, a warning appears after you sign in at Apple’s account website.
The Lock Screen message warns: “Apple detected a mercenary spyware attack targeted at your iPhone. There are actions you can take now to protect your data and device.” That wording is alarming for a reason. Apple says mercenary spyware attacks are far more sophisticated than the malware and scams most of us encounter. Attackers can spend extraordinary amounts of money targeting a very small number of people.
The good news is that receiving a warning does not automatically mean the spyware successfully broke into your device. It means Apple detected activity indicating that you were individually targeted. Still, this isn’t an alert I would ignore.
Who is being targeted with mercenary spyware?
Most iPhone owners will probably never encounter one of these warnings. Apple says these attacks have historically targeted people because of who they are or what they do. Past targets have included journalists, activists, politicians and diplomats. The attacks have also been linked through public research and reporting to state actors and private companies that develop surveillance tools on their behalf.
Apple does not identify a specific attacker or country when it sends a notification. The company says revealing too much about how it detects these campaigns could help spyware operators change their methods.
How to tell whether an Apple spyware warning is real
This part is especially important because you can bet scammers will try to copy these warnings. A fake alert could claim your iPhone was hacked and then send you to a phony Apple login page. The crook’s real goal may be stealing your Apple Account credentials.
Apple says its genuine threat notifications will never ask you to click a link, open a file, install an app or profile, or give someone your Apple Account password or verification code by email or phone.
Rather than trusting an unexpected email, open your browser yourself and go directly to Apple’s official account website. Sign in normally. If Apple really sent you a threat notification, the warning should appear at the top of your Apple Account page.
What to do if Apple says spyware targeted your iPhone
If you receive a genuine warning, I would treat your phone as a potential security incident until you know more. Here are the steps I recommend.
APPLE AI SECURITY UPDATE PROVES HACKERS MOVE FAST
Apple’s updated spyware alerts warn targeted iPhone users on the Lock Screen and recommend immediate security steps, including turning on Lockdown Mode.
1) Update your iPhone immediately
Go to Settings> General> Software Update and install the latest available version of iOS. Security updates frequently close vulnerabilities that sophisticated attackers may try to exploit. Apple reinforced that recommendation in its statement to CyberGuy, saying, “Turning on Lockdown Mode and keeping devices updated with the latest software are critical defenses for protecting against mercenary spyware attacks.”
2) Turn on Lockdown Mode
Apple specifically recommends Lockdown Mode for people who receive a mercenary spyware warning. Apple says its updated notification experience is designed to make it easier for recipients to access recommended protective steps, including enabling Lockdown Mode.
On an iPhone or iPad:
Open Settings
Tap Privacy & Security
Scroll down and tap Lockdown Mode
Tap Turn On Lockdown Mode
Choose Turn On & Restart, then enter your passcode
Lockdown Mode deliberately restricts certain apps, websites and connections to reduce the number of ways highly sophisticated spyware can attack your device. An Apple spokesperson said in March 2026 that the company was not aware of any successful mercenary spyware attack against an Apple device while Lockdown Mode was enabled. That does not make any security feature unbeatable, but it is a remarkable record for a tool designed specifically for people facing this kind of threat. For a closer look, see our guide on how to protect your iPhone with Lockdown Mode.
3) Secure your Apple Account
Make sure two-factor authentication (2FA) is enabled and review the devices connected to your Apple Account. Also use a strong password that you do not reuse anywhere else. A password manager can generate and store unique passwords so one stolen credential does not put several accounts at risk.
4) Be suspicious of follow-up messages
Once a warning like this gets public attention, scammers can exploit the fear around it. Do not trust someone who suddenly calls claiming to be Apple Support. Avoid clicking links in unexpected texts or emails about spyware. Remember, Apple says its threat notifications will never ask for your password or verification code.
5) Watch for signs your phone may have been compromised
Strange behavior alone does not prove spyware is installed. However, unexplained apps, settings you did not change or other unusual activity deserve attention. Here are more signs that may indicate your phone has been hacked and what you can do next.
Should everyone turn on Lockdown Mode?
Probably not. Apple describes Lockdown Mode as an “extreme” protection intended for the relatively small number of people who face sophisticated targeted attacks. Some websites and Apple features work differently while it is enabled. For most people, keeping software current and protecting your Apple Account will provide a more practical everyday security foundation. However, the calculation changes if Apple sends you a mercenary spyware notification. Apple now specifically tells CyberGuy that turning on Lockdown Mode and keeping devices updated are “critical defenses” against mercenary spyware attacks.
Tips to keep your Apple devices safer
Even if you never see a spyware warning, there are several steps worth taking now.
Keep your software updated
Security fixes can close vulnerabilities before attackers get another chance to exploit them. Apple recommends keeping your devices updated with the latest software.
On an iPhone or iPad:
Open Settings
Tap General
Tap Software Update
If an update is available, tap Download and Install
Follow the onscreen instructions
You can also tap Automatic Updates from the Software Update screen to help keep future updates installed automatically.
ARE APPLE DEVICES SPYING? WHAT YOUR IPHONE TRACKS
Apple urges users who receive a genuine mercenary spyware warning to update their devices, enable Lockdown Mode and secure their Apple Accounts.(Photo by Kevin Carter/Getty Images)
On a Mac:
Click the Apple menu
Choose System Settings
Click General
Click Software Update
Install any available update and follow the onscreen instructions
Use Face ID, Touch ID or a strong device passcode
Avoid an easy-to-guess four-digit code. These iPhone security settings can help protect your device.
Turn on two-factor authentication (2FA)
This adds another barrier if someone obtains your Apple Account password. Here’s how two-factor authentication works and how to enable it.
Enable Stolen Device Protection
Apple recommends this as part of its broader security guidance. Here’s how to turn on Stolen Device Protection on your iPhone.
Install apps from the App Store
Be extremely cautious with profiles or software someone tells you to install. You can also check your iPhone for suspicious configuration profiles or device management settings.
Slow down when a message creates urgency
Unexpected security warnings can also be bait used in phishing attacks. Here’s how to spot fake Apple alerts and phishing messages.
Use strong security software
Good security software can help protect you from malicious links, phishing attempts and other online threats that may try to steal your information. Get my picks for the best 2026 antivirus protection winners for your Windows, Mac, Android & iOS devices at Cyberguy.com
Reduce your online footprint with a data removal service
Data brokers can collect and sell information such as your phone number, address and other personal details. A data removal service can help remove that information from people-search and broker sites. It will not stop mercenary spyware, but reducing how much personal information is publicly available can give bad actors less information to work with. Check out my top picks for data removal services and get a free scan to find out if your personal information is already out on the web by visiting Cyberguy.com.
Consider identity theft protection
If someone gains access to sensitive personal or financial information, identity theft protection can help monitor for signs that your information is being misused and provide recovery assistance if fraud occurs. It will not prevent spyware from infecting an iPhone, but it adds another layer of protection around your identity. See my tips and best picks on Best Identity Theft Protection at Cyberguy.com.
Kurt’s key takeaways
Apple bringing these warnings directly to the iPhone Lock Screen is a smart move. A warning this serious should be difficult to miss or mistake for an ordinary email. Apple’s response to CyberGuy also makes clear what it wants targeted users to do next: take the notification seriously, enable Lockdown Mode and get the latest software onto their devices. There is another takeaway here that affects far more people than those receiving these alerts. Sophisticated spyware was once something most of us associated with intelligence agencies and highly unusual cases. The commercial spyware industry has made these tools available to a wider range of operators and Apple says the attacks remain global. Most of us are unlikely to become targets of mercenary spyware. That should be reassuring. Still, Apple’s warnings show just how aggressive targeted surveillance can become when someone has enough resources and determination. If Apple ever tells you that you have been targeted, believe the warning until qualified experts give you a reason not to.
Do you think Apple is doing enough to protect people from sophisticated spyware, or should stronger protections be turned on by default? Let us know by writing to us at Cyberguy.com.
Sign up for my FREE CyberGuy Report
Get my best tech tips, urgent security alerts and exclusive deals delivered straight to your inbox.
For simple, real-world ways to spot scams early and stay protected, visit CyberGuy.com– trusted by millions who watch CyberGuy on TV daily.
Plus, you’ll get instant access to my Ultimate Scam Survival Guide free when you join.
CLICK HERE TO DOWNLOAD THE FOX NEWS APP
Copyright 2026 CyberGuy.com. All rights reserved.
Kurt “CyberGuy” Knutsson is an award-winning tech journalist who has a deep love of technology, gear and gadgets that make life better with his contributions for Fox News & FOX
Advertisement Singapore Artistes can express humanitarian concerns, but not undermine public order and security: Tan Kiat How Senior Minister of State Tan Kiat How cited several performances dealing with social and humanitarian issues that had been allowed to proceed in Singapore. Robert Del Naja and Grant Marshall from Massive Attack stand with a Palestinian flag
Published
1 day ago
in
By
Advertisement
Singapore
Artistes can express humanitarian concerns, but not undermine public order and security: Tan Kiat How
Senior Minister of State Tan Kiat How cited several performances dealing with social and humanitarian issues that had been allowed to proceed in Singapore.
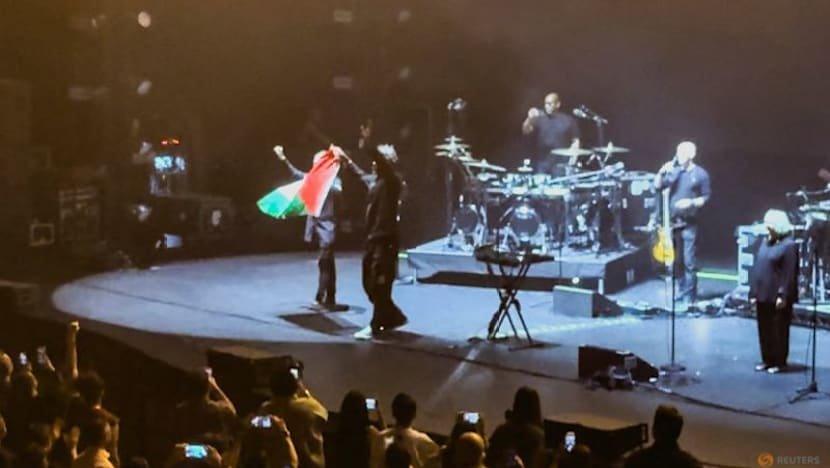
Robert Del Naja and Grant Marshall from Massive Attack stand with a Palestinian flag onstage at the end of their performance in Singapore, July 29, 2026, in this screengrab from video obtained from social media. Simran Panaech/via REUTERS
Add CNA as a trusted source to help Google better understand and surface our content in search results.
Read a summary of this article on FAST.
Get bite-sized news via a new cards interface. Give it a try.
Click here to return to FAST Tap here to return to FAST
FAST
SINGAPORE: Artistes can express humanitarian concerns about international conflicts, but such expression should not undermine public order, security or stability in Singapore, Senior Minister of State for Digital Development and Information Tan Kiat How said on Thursday (Sep 10).
“Singapore should not be used by foreigners as a platform to further political causes, including those relating to conflicts or political issues overseas,” he said.
Artistes, whether Singaporean or foreign, are expected to abide by Singapore’s laws and the conditions of the arts entertainment licence when performing here, he added.
Mr Tan was responding in parliament to MP Hazlina Abdul Halim (PAP-East Coast), who asked how authorities distinguish prohibited political advocacy from expressions of humanitarian concern.
CNA Games
Guess Word
Crack the word, one row at a time
Buzzword
Create words using the given letters
Mini Sudoku
Tiny puzzle, mighty brain teaser
Mini Crossword
Small grid, big challenge
Word Search
Spot as many words as you can
Show More
Show Less
She also asked how an artiste’s intent and the context of an expression are taken into account, and whether licensing conditions would be reviewed to exclude peaceful expressions of support for humanitarian causes.
Mr Tan said that besides an artiste’s intention, the Infocomm Media Development Authority (IMDA) considers the likely impact of a performance when assessing whether it meets licensing conditions.
Under IMDA’s Arts Entertainment Classification Code, content should not undermine public order, national security or stability.
The code, which sets out the framework for assessing and classifying live or public arts entertainment, also states that content should be “sensitive to the concerns of different racial or religious groups and the prevailing community expectations of what is necessary to safeguard racial harmony and religious harmony”.
In July, members of British band Massive Attack were issued stern warnings and barred from re-entering Singapore after flying a Palestinian flag during a concert, with one of the members shouting “Free Palestine”.
06:31 Min
The government recognises the humanitarian impact of international conflicts and that artistes may wish to express concern for those affected. Such expressions are not prohibited but should not undermine public order, national security or stability in Singapore. This condition is made clear in the Arts Entertainment Classification Code issued by the Infocomm Media Development Authority. Senior Minister of State for Digital Development and Information Tan Kiat How highlighted this approach in reply to an MP’s questions in parliament on Thursday (Sep 10). He stressed that Singapore should not be used by foreigners as a platform to further political causes, including those relating to conflicts or political issues overseas.
Ms Hazlina asked Mr Tan for examples of performances involving social causes that had been allowed to take place.
He cited To The Unforgotten, an event held in May this year that featured a song, poem and multimedia artwork about the Israel-Gaza conflict. It was classified R18.
Another example was 6 Microlectures on Genocides. Also classified R18, the play comprised short works that explore themes of genocide, war crimes and contemporary conflicts, Mr Tan said.
He also pointed to the 2024 stand-up comedy show Namaste, which was classified Advisory 16 and included a segment in which comedians spoke about the Israel-Gaza conflict.
“So having material and content on causes itself is not prohibited, and the licensing framework is designed to, of course, protect young people from unwanted content, but also allow people to make decisions on what they can watch,” said Mr Tan.
“But at the same time, having some boundaries on the kind of content that may stir up public disorder or national security considerations.”
Mr Tan said assessments were “very contextual” and encouraged applicants for Arts Entertainment Licences to engage IMDA early.
“The earlier the applicants engage IMDA, the earlier conversations can start, and earlier we can give clarity and guidance on the kind of content that may be approved and
Trezor warned users that attackers used a compromised third-party email provider to send a fake STM32 security alert, a phishing scam that also hit rival BitBox and other Bitcoin companies. The post Trezor Email Provider Breached in Phishing Attack Targeting Crypto Users appeared first on Crypto News Australia…
Published
1 day ago
in
By
Trezor warned users that attackers used a compromised third-party email provider to send a fake STM32 security alert, a phishing scam that also hit rival BitBox and other Bitcoin companies.
The post Trezor Email Provider Breached in Phishing Attack Targeting Crypto Users appeared first on Crypto News Australia… Read More
Payward has agreed to acquire Magic Labs’ wallet-as-a-service business, adding embedded, non-custodial wallets to the infrastructure platform behind Kraken. The deal brings technology used to create more than 60 million wallets into Payward’s expanding enterprise product suite. Newton Labs Sells Magic Wallet Business to Focus Fully on Onchain Authorization Payward…
Published
2 days ago
in
By
Payward has agreed to acquire Magic Labs’ wallet-as-a-service business, adding embedded, non-custodial wallets to the infrastructure platform behind Kraken. The deal brings technology used to create more than 60 million wallets into Payward’s expanding enterprise product suite. Newton Labs Sells Magic Wallet Business to Focus Fully on Onchain Authorization Payward… Read More